
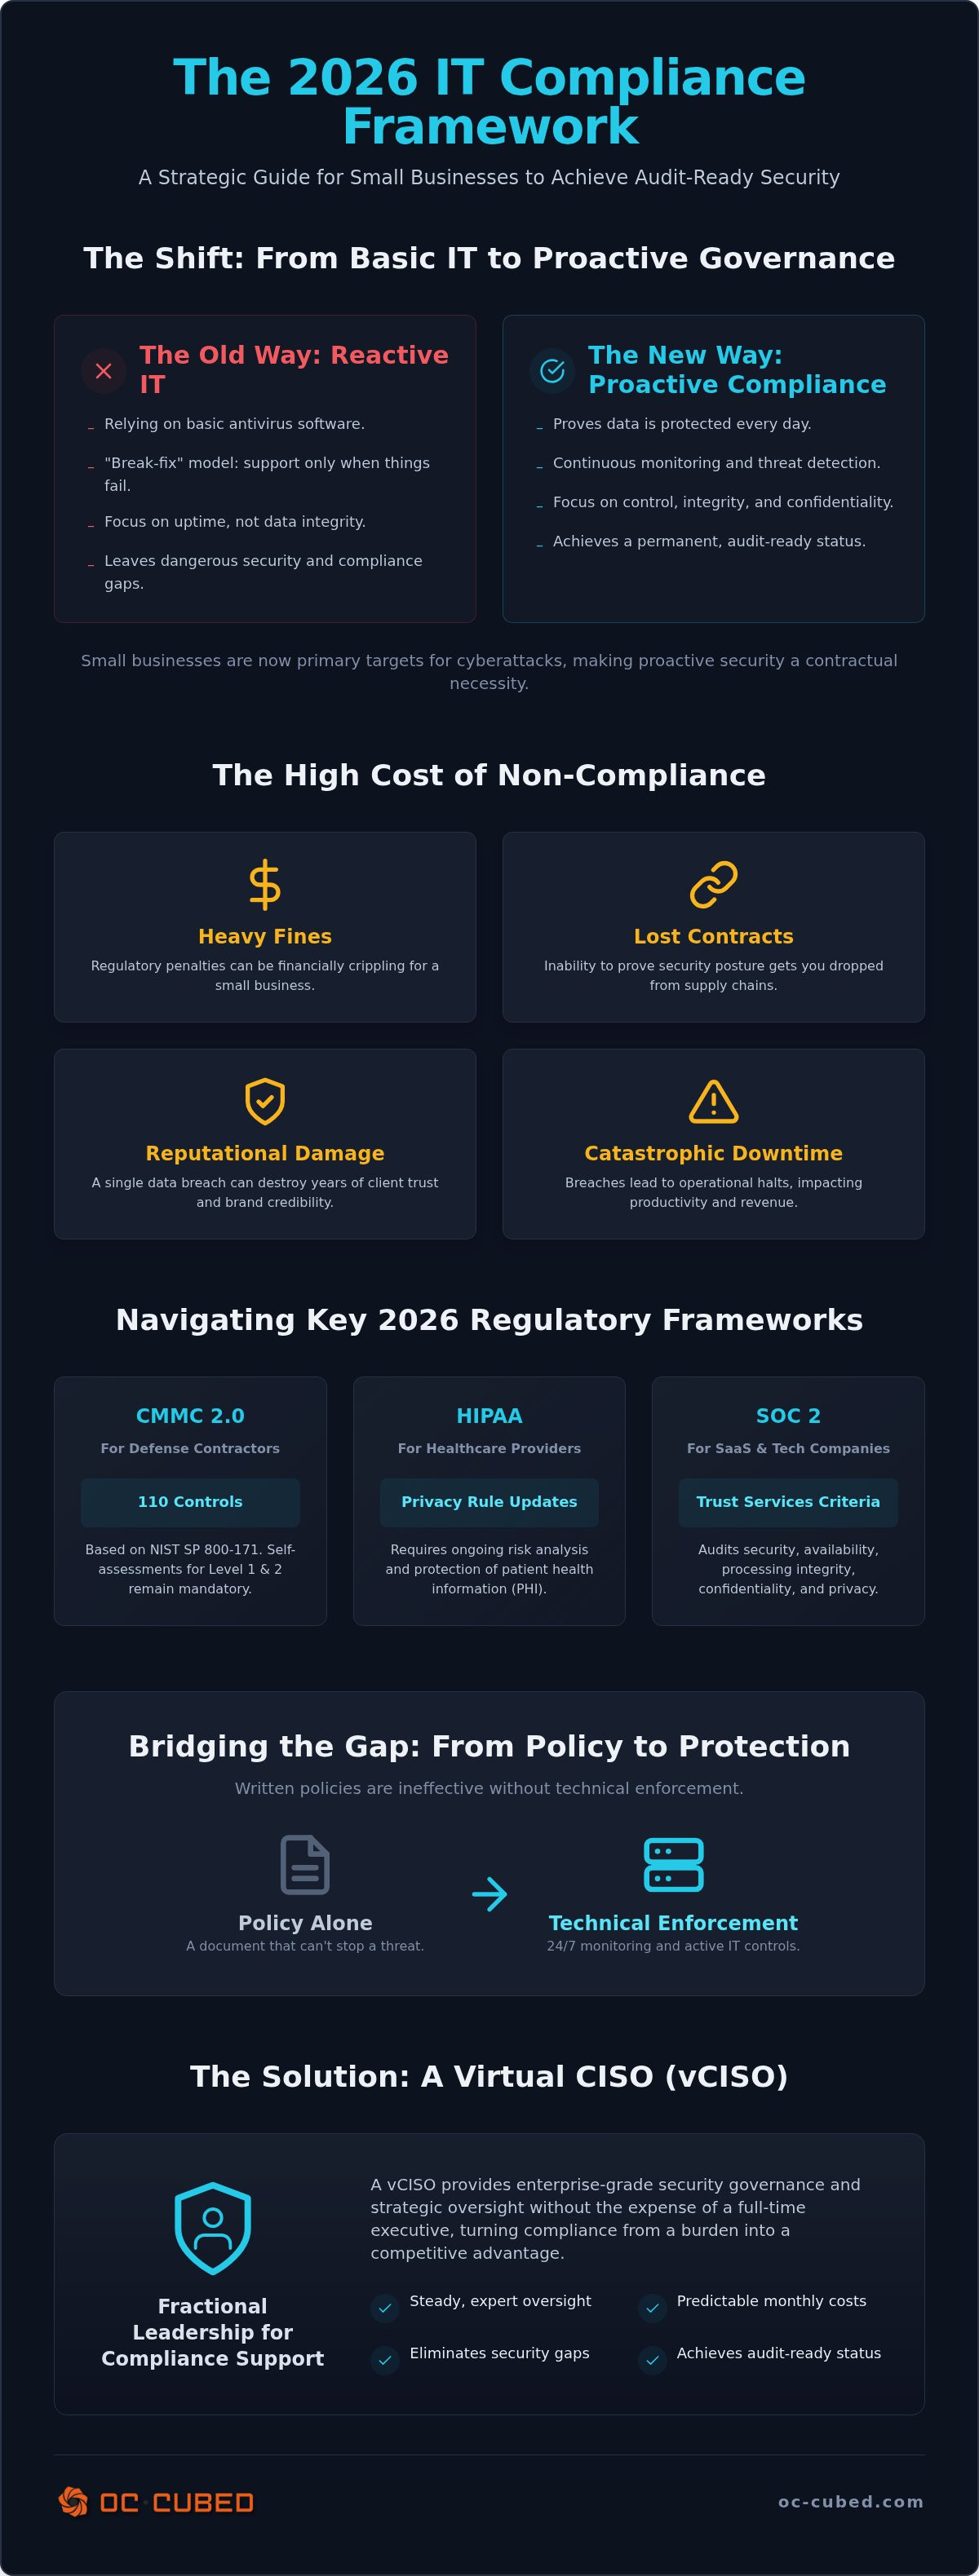
Your basic antivirus software is not a compliance strategy. It's a common mistake that leaves many firms vulnerable to heavy fines and lost contracts. Relying on software alone won't satisfy a CMMC auditor or a HIPAA risk analysis. You need a strategy that proves you're protecting data every single day. It's about control and protection, not just installation.
It's exhausting to keep up with shifting mandates. You've likely felt the pressure of proving your security posture just to stay eligible for government or enterprise work. When the Department of War suspends one requirement while keeping others mandatory, it's easy to feel overwhelmed. This guide provides a clear 2026 strategic framework for IT compliance support small business DC to help you move from reactive fixes to proactive governance. You'll learn how to secure your network and achieve audit-ready status without the overhead of a full-time executive.
We'll explore the current requirements for CMMC self-assessments, upcoming HIPAA Privacy Rule updates, and how a Virtual CISO provides the steady oversight you need to grow. You can achieve predictable costs and true peace of mind through fractional leadership. We'll show you how to turn compliance from a burden into a competitive advantage.
Key Takeaways
- Understand why small businesses are the primary targets for cyberattacks in 2026 and how to shift from reactive repairs to proactive security.
- Navigate the latest 2026 updates to CMMC 2.0 and HIPAA with professional IT compliance support small business DC that protects your contracts.
- Learn why written compliance policies are ineffective without 24/7 network monitoring and technical enforcement to back them up.
- Discover how a Virtual CISO provides enterprise-grade security governance and strategy without the expense of a full-time hire.
- Transition to an audit-ready status with a predictable monthly retainer that eliminates surprise IT costs and security gaps.
The Evolution of Small Business IT Compliance in 2026
IT compliance is no longer just a checklist for the legal department. In 2026, it represents the critical intersection where legal mandates meet technical execution. For many leaders, IT compliance support small business DC has become the foundation of their operational stability. Compliance ensures that your technical environment actually does what your policies say it does. This shift is driven by a harsh reality. Small businesses are now the primary targets for cyberattacks because they often serve as the entry point into larger enterprise networks.
We've seen a total move from "optional security" to "contractual compliance." Large enterprises and government agencies now demand proof of security before signing a contract. You aren't just protecting your own data; you're protecting your access to the market. Proactive security creates a barrier against these threats, while reactive IT support only attempts to clean up the mess after the damage is done. True protection requires a framework of Information Technology (IT) controls that monitor your network around the clock.
Why Basic IT Support is No Longer Enough
There's a massive difference between keeping your computers running and protecting sensitive data. Basic support focuses on uptime and convenience. Compliance focuses on integrity and confidentiality. If your technician only shows up when something breaks, your security is already failing. This "break-fix" model leaves dangerous gaps that auditors will quickly identify. It's a reactive approach that doesn't account for the sophisticated threats of 2026.
Modern firms need consistent oversight. Specialized remote IT management services bridge this gap for distributed teams. They provide the continuous visibility required to meet modern standards. You need a partner who understands that a functioning laptop isn't the same as a secure one. Expert IT compliance support small business DC ensures your team stays productive without compromising your regulatory standing or your peace of mind.
The Cost of Non-Compliance: More Than Just Fines
Fines are expensive, but they aren't the only risk. The true cost of non-compliance is often the loss of business opportunities. Supply Chain Risk Management has become a standard auditing practice for most industries. If you can't prove your security posture, you'll be dropped from lucrative contracts. Your customers are auditing you because their own compliance depends on your safety. They won't take a chance on a vendor with weak protocols.
Reputational damage is often permanent. A single breach can destroy years of trust with your clients. Implementing security threat detection and remediation prevents catastrophic downtime and keeps your brand intact. It's about control. When you have the right systems in place, you don't have to fear the next audit. You can focus on growth while we handle the protection. This steady reliability is what allows a business to scale with confidence.
Navigating Key Regulatory Frameworks: CMMC, HIPAA, and SOC2
Not all compliance is created equal. A defense contractor faces different hurdles than a healthcare provider or a SaaS startup. The key is understanding which framework applies to your growth path. Seeking IT compliance support small business DC allows you to identify these requirements early. Many firms treat audits as a yearly hurdle. The best approach is continuous compliance. This ensures you're always ready, rather than scrambling every twelve months. Foundationally, consistent Microsoft 365 tenant maintenance is vital. It secures your core communication and data storage against unauthorized access. Aligning with FTC cybersecurity guidance helps establish a baseline for these more rigorous standards.
CMMC 2.0: The Standard for Defense Contractors
As of August 2026, the CMMC landscape has shifted. The Department of War suspended mandatory third-party assessments for Phase II on July 13, 2026. However, self-assessments for Level 1 and Level 2 remain mandatory. You must still implement the 110 security controls from NIST SP 800-171 Revision 2. This requires professional IT compliance support small business DC to manage the technical complexities. Proper firewall and switch management is non-negotiable. It creates the secure boundary needed to protect Controlled Unclassified Information (CUI). Managed security ensures these controls stay active and documented.
HIPAA and SOC2: Protecting Privacy and Trust
Healthcare providers must stay alert to the HIPAA Privacy Rule update expected in August 2026. While the Security Rule overhaul is delayed until 2027, enforcement on risk analysis remains strict. Technical safeguards must extend beyond the office in our remote work era. For tech firms, SOC2 Type II reporting is the gold standard for building trust. It proves your systems are secure over a period of time, not just for a single day. Modern audits now emphasize zero-trust principles and continuous monitoring. Protecting Personally Identifiable Information (PII) starts with the inbox. Email security with Proofpoint is a critical control for preventing data leaks. If you need to verify your current standing, we can provide expert compliance guidance tailored to your industry.
Bridging the Gap: Moving from Policy to Technical Protection
Written policies are just paper until they're enforced by technical controls. An auditor won't just ask to see your handbook; they'll ask for the logs that prove you followed it. This is why IT compliance support small business DC is a technical discipline, not just a legal one. You need 24/7 network monitoring and configuration to ensure your environment stays within the required parameters at all hours. If a setting drifts or a firewall rule changes, you need to know immediately. Real-time visibility is the only way to maintain a state of continuous compliance.
Endpoint protection and antivirus serve as your first line of defense. These tools prevent the initial breach that leads to a catastrophic compliance failure. However, protection is only half the battle. You must also prove that these defenses were active during a specific timeframe. Monthly reporting provides the evidence auditors require to verify your security posture. It turns technical data into a readable format that demonstrates your commitment to safety. Following CISA's Cyber Guidance helps shift your business from static plans to active, verifiable defenses that stand up to scrutiny.
Securing the Cloud: Microsoft 365 and Beyond
Cloud security depends heavily on your subscription level. Proper Microsoft 365 license management for small business ensures you have access to the advanced features required for frameworks like CMMC or HIPAA. Default settings in cloud tenants are often too permissive because they favor convenience over strict security. Closing these gaps requires consistent helpdesk and NOC integration. This ensures that every configuration change is monitored and aligned with your compliance goals. We manage the tenant so you can manage your growth.
Vendor Management as a Compliance Requirement
Your security is only as strong as your weakest vendor. Small businesses are now required to audit their own software and service providers to prevent supply chain vulnerabilities. This is a critical component of IT compliance support small business DC. Centralized vendor management prevents "shadow IT," which occurs when employees use unapproved apps that bypass your security controls. Professional fractional CIO for small business leadership handles this oversight for you. It removes the burden of vetting complex service level agreements while ensuring your entire digital supply chain remains secure and compliant.
The Virtual CISO: Fractional Leadership for Compliance Support
Small businesses often lack the budget for a full-time security executive, yet they face the same complex threats as global corporations. A Virtual CISO (vCISO) solves this problem by providing elite security governance on a fractional basis. This role differs significantly from a vCIO. While the vCIO focuses on infrastructure and general strategy, the vCISO is strictly dedicated to managing your risk and security posture. They oversee security threat detection and remediation, ensuring that every alert is handled with professional precision. This is the most efficient way to secure IT compliance support small business DC without inflating your payroll.
Why Your Business Needs a Fractional CISO in 2026
The cybersecurity talent shortage is a documented reality in 2026. Hiring a qualified full-time leader can cost hundreds of thousands in compensation alone. Choosing IT leadership without full-time hire allows you to access that same level of expertise at a fraction of the cost. A fractional CISO for small business provides an objective, unbiased view of your technical risks. They don't have internal political ties or "the way we've always done it" mentalities. Instead, they bring a results-driven perspective that prioritizes protection and contractual compliance.
Governance, Risk, and Compliance (GRC) Leadership
Compliance requires more than just tools; it requires a System Security Plan (SSP). This document is your roadmap for how you meet every regulatory control. Your vCISO takes ownership of this plan, keeping it current as your network evolves. They also lead the charge during third-party audits, acting as your expert representative. This leadership ensures your team is prepared and your documentation is flawless. You gain the confidence of executive-level reporting, which is vital for reassuring stakeholders and boards that your growth is secure. Expert IT compliance support small business DC ensures you're never caught off guard by a surprise audit or a new regulation.
Implementing a Compliance-First IT Strategy with OC Cubed
Moving from a reactive mindset to a compliance-first strategy is the most significant step a small business can take in 2026. It's about stability. When you choose IT compliance support small business DC, you aren't just buying software. You're investing in a system that protects your growth and secures your contracts. The transition begins by replacing unpredictable emergency visits with a Monthly Managed IT Services Retainer. This model ensures that security is baked into your operations from day one. It shifts the focus from fixing problems to preventing them entirely.
Our onboarding process for remote IT support is deliberate and thorough. We integrate security threat detection and remediation tools across your entire network. This phase is overseen by virtual project management experts who ensure every compliance upgrade is implemented without disrupting your workflow. They manage the technical details of firewall and switch management while coordinating with your internal teams. It's a structured approach that removes the anxiety of technical transitions. You get a clear timeline and a dedicated team that understands your specific regulatory environment.
The Monthly Retainer: Predictable Costs, Proactive Protection
Surprise IT bills can cripple a small business budget. Our all-inclusive management model eliminates these fluctuations. We bundle essential services into one predictable monthly fee. This includes:
- Microsoft 365 Tenant Maintenance to keep your cloud environment secure.
- Endpoint Protection and antivirus to stop threats at the source.
- 24/7 Network Monitoring to identify and resolve issues instantly.
- Email Security with Proofpoint to protect your team from phishing.
- Monthly Reporting so you have proof of compliance for auditors.
This allows you to allocate resources toward growth instead of emergency repairs. You gain a partner who is incentivized to keep your system running perfectly. Steady reliability is the goal of our retainer model.
Next Steps: Securing Your Business for 2026
Evaluating your current compliance posture is the first task. Many businesses discover they have gaps in their NIST 800-171 controls or HIPAA risk analysis only after an incident occurs. Proactive leaders start with a comprehensive security audit led by a vCISO. This assessment identifies vulnerabilities and provides a clear roadmap for remediation. You'll move forward with the peace of mind that your IT compliance support small business DC is handled by experts who care about your results. We provide the documentation and leadership needed to prove your status to any auditor or stakeholder.
Securing Your Competitive Edge in 2026
Compliance in 2026 is no longer a choice; it's a requirement for doing business with the government and major enterprises. You've seen how the right IT compliance support small business DC turns a regulatory burden into a growth engine. By moving from reactive "break-fix" repairs to a proactive model, you protect your reputation and your bottom line. It's about having the right controls in place before an auditor ever knocks on your door.
Implementing a strategic framework involves more than just software. It requires the steady hand of fractional executive leadership. You gain access to enterprise-grade security strategy and 24/7 monitoring through NOC integration without the overhead of a full-time hire. This approach provides the control and peace of mind necessary to scale your operations with confidence. Your team can focus on innovation while experts manage the governance and remediation.
Your business deserves a protector that understands the high stakes of modern data security. We are ready to help you navigate these complex requirements with steady reliability. Let's build a secure future together.
Frequently Asked Questions
What is the difference between IT support and IT compliance support?
Standard IT support focuses on uptime and hardware functionality. Compliance support focuses on risk mitigation and meeting specific regulatory standards like CMMC or HIPAA. While regular support fixes a printer, compliance support ensures every data transfer is encrypted and logged. It is about maintaining verifiable technical controls. This distinction is vital for IT compliance support small business DC because it moves your focus from convenience to legal protection.
Does my small business really need a Virtual CISO?
Yes, if you handle sensitive government or healthcare data. A Virtual CISO provides the executive-level oversight required for security governance without the high salary of a full-time hire. They take accountability for your System Security Plan and risk assessments. This leadership ensures your technical team follows a cohesive strategy. It is the most efficient way to gain enterprise-grade security leadership while staying within a small business budget.
How much does it cost to become CMMC compliant in 2026?
Costs vary based on your current security maturity and the level of certification required. While we don't quote specific prices, the Department of Defense has noted that implementing the 110 controls of NIST SP 800-171 is the primary driver of expense. You will need to account for technical upgrades, ongoing monitoring, and documentation. Investing in IT compliance support small business DC through a retainer model helps spread these costs over time.
Can remote IT support handle complex compliance requirements?
Absolutely. Compliance is primarily a digital and configuration task rather than a physical hardware task. Remote support teams manage firewall settings, cloud tenant security, and endpoint protection from a central location. This allows for 24/7 network monitoring and rapid threat remediation regardless of your office location. Remote management also ensures that all security logs are centralized and ready for an auditor to review at any time.
What is the first step in a small business compliance audit?
The first step is a comprehensive gap analysis. This involves comparing your current IT environment against the specific requirements of your target framework, such as HIPAA or CMMC 2.0. You must identify where your technical controls and written policies fall short. This audit creates a prioritized roadmap for remediation. Starting with an expert-led assessment ensures you don't waste resources on unnecessary tools that don't satisfy your specific regulatory needs.
How does Microsoft 365 help with industry compliance?
Microsoft 365 provides the underlying infrastructure for secure data storage and communication. Depending on your license level, it includes advanced features like Data Loss Prevention and encrypted email. However, the software isn't compliant out of the box. You must perform regular Microsoft 365 tenant maintenance to configure these settings correctly. Proper management ensures your cloud environment meets the strict standards for confidentiality and integrity required by modern auditors.
Is antivirus software enough to meet SOC2 or HIPAA standards?
No, antivirus is only one small component of a larger security framework. While endpoint protection is necessary, SOC2 and HIPAA require much more. You need documented risk assessments, employee training, and strict access controls. You must also prove that you are monitoring your network for unauthorized changes. Antivirus stops certain malware, but compliance requires a comprehensive system of governance that protects the entire lifecycle of sensitive data.
What is the benefit of a monthly managed IT retainer for compliance?
A monthly retainer provides predictable costs and proactive protection. Unlike the "break-fix" model, a retainer ensures your systems are constantly monitored and maintained. This eliminates surprise bills and ensures your security controls never lapse. It also includes the ongoing reporting and documentation needed to prove compliance during an audit. This steady reliability allows you to focus on your core business growth while we handle the technical and regulatory details.


